Without a Content-Security-Policy header, the browser runs any script that ends up in your page, including one an attacker injected.Exorcise it today: Check your response headers for Content-Security-Policy. Start in report-only mode, read the reports, then enforce it.How a public-page review works, step by step: carlosandmunoz.com/qa-review-guide.html#Halloween #CyberSecurity #Vulnerability #QA #CSP #QAlab
🎃 The missing CSP: anything can crawl in.

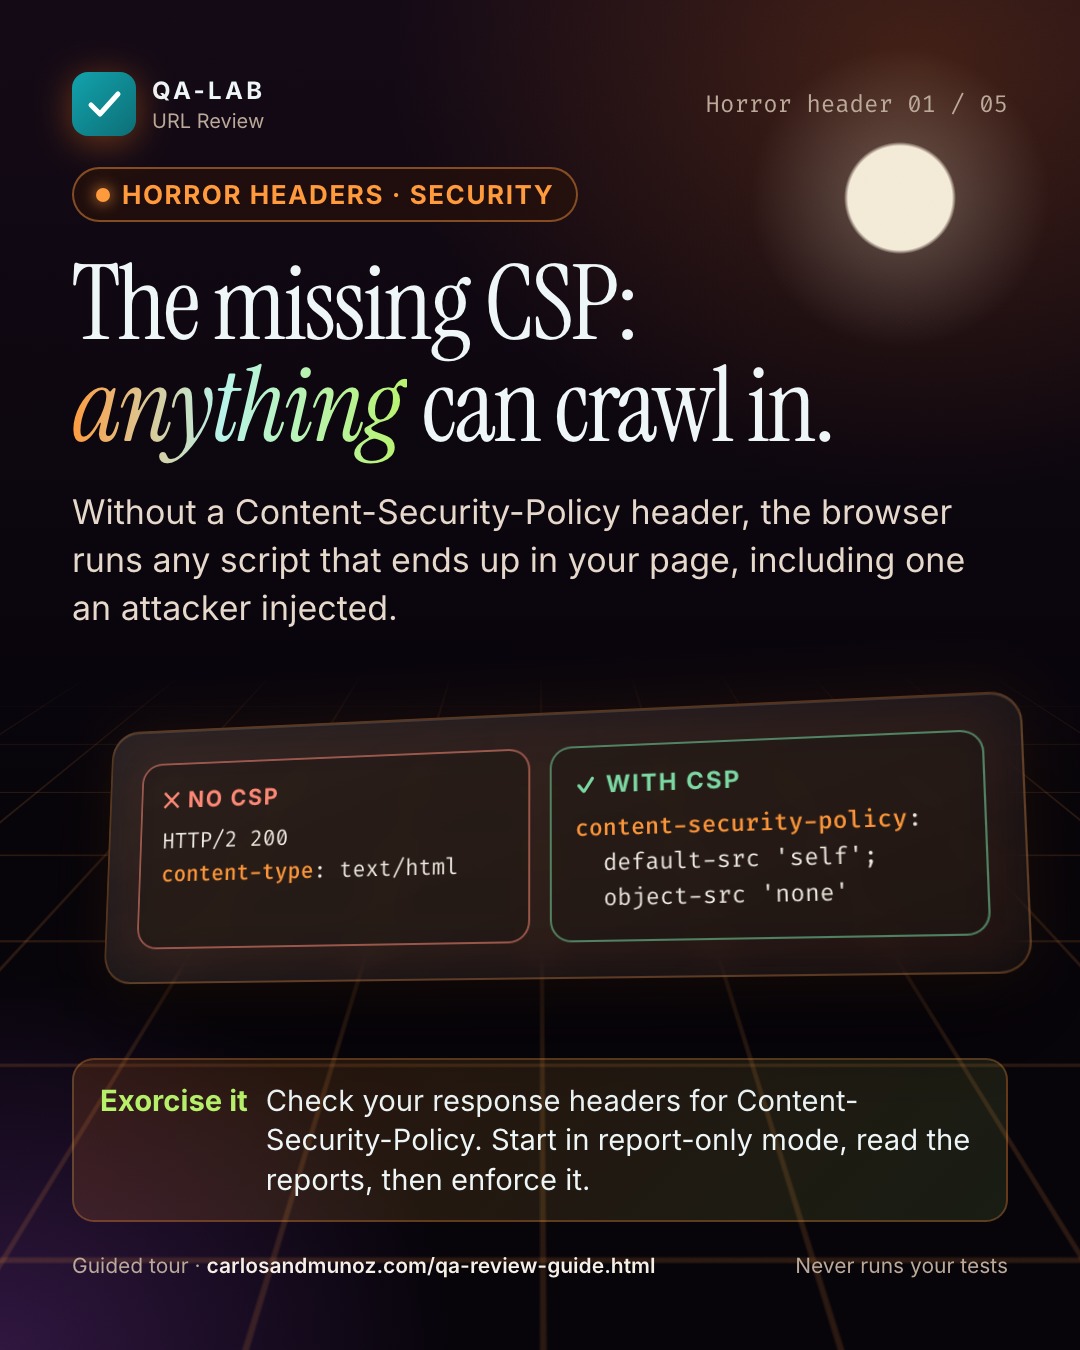
Without a Content-Security-Policy header, the browser runs any script that ends up in your page, including one an attacker injected.

Exorcise it today: Check your response headers for Content-Security-Policy. Start in report-only mode, read the reports, then enforce it.

How a public-page review works, step by step: https://carlosandmunoz.com/qa-review-guide.html?utm_source=linkedin&utm_medium=social&utm_campaign=horror-headers-2026-10&utm_content=missing-csp

#Halloween #CyberSecurity #Vulnerability #QA #CSP #QAlab
X
🎃 The missing CSP: anything can crawl in.

Check your response headers for Content-Security-Policy. Start in report-only mode, read the reports, then…

carlosandmunoz.com/qa-review-guide?utm_source=x&utm_medium=social&utm_campaign=horror-headers-2026-10&utm_content=missing-csp
Instagram
🎃 The missing CSP: anything can crawl in.

Without a Content-Security-Policy header, the browser runs any script that ends up in your page, including one an attacker injected.

Exorcise it: Check your response headers for Content-Security-Policy. Start in report-only mode, read the reports, then enforce it.

Full guide: link in bio.

#Halloween #CyberSecurity #QA #CSP #QAlab
Facebook
🎃 The missing CSP: anything can crawl in.

Without a Content-Security-Policy header, the browser runs any script that ends up in your page, including one an attacker injected.

Exorcise it: Check your response headers for Content-Security-Policy. Start in report-only mode, read the reports, then enforce it.

https://carlosandmunoz.com/qa-review-guide.html?utm_source=facebook&utm_medium=social&utm_campaign=horror-headers-2026-10&utm_content=missing-csp

#Halloween #Vulnerability #QA #QAlab
TikTok
🎃 The missing CSP: anything can crawl in. Check your response headers for Content-Security-Policy. Start in report-only mode, read the reports, then enforce it. #Halloween #CyberSecurity #Vulnerability #QA #CSP #WebSecurity #WebDev #QAlab
YouTube
Without a Content-Security-Policy header, the browser runs any script that ends up in your page, including one an attacker injected.

Exorcise it: Check your response headers for Content-Security-Policy. Start in report-only mode, read the reports, then enforce it.

Guide: https://carlosandmunoz.com/qa-review-guide.html?utm_source=youtube&utm_medium=social&utm_campaign=horror-headers-2026-10&utm_content=missing-csp

Horror header 1/5 · QA-lab URL Review

#Halloween #DevOps #CyberSecurity #QA #CSP #WebSecurity #Programming #LearnOnYouTube #QualityAssurance #InfoSec #TestAutomation #QAlab