Your public response headers say more than you think.
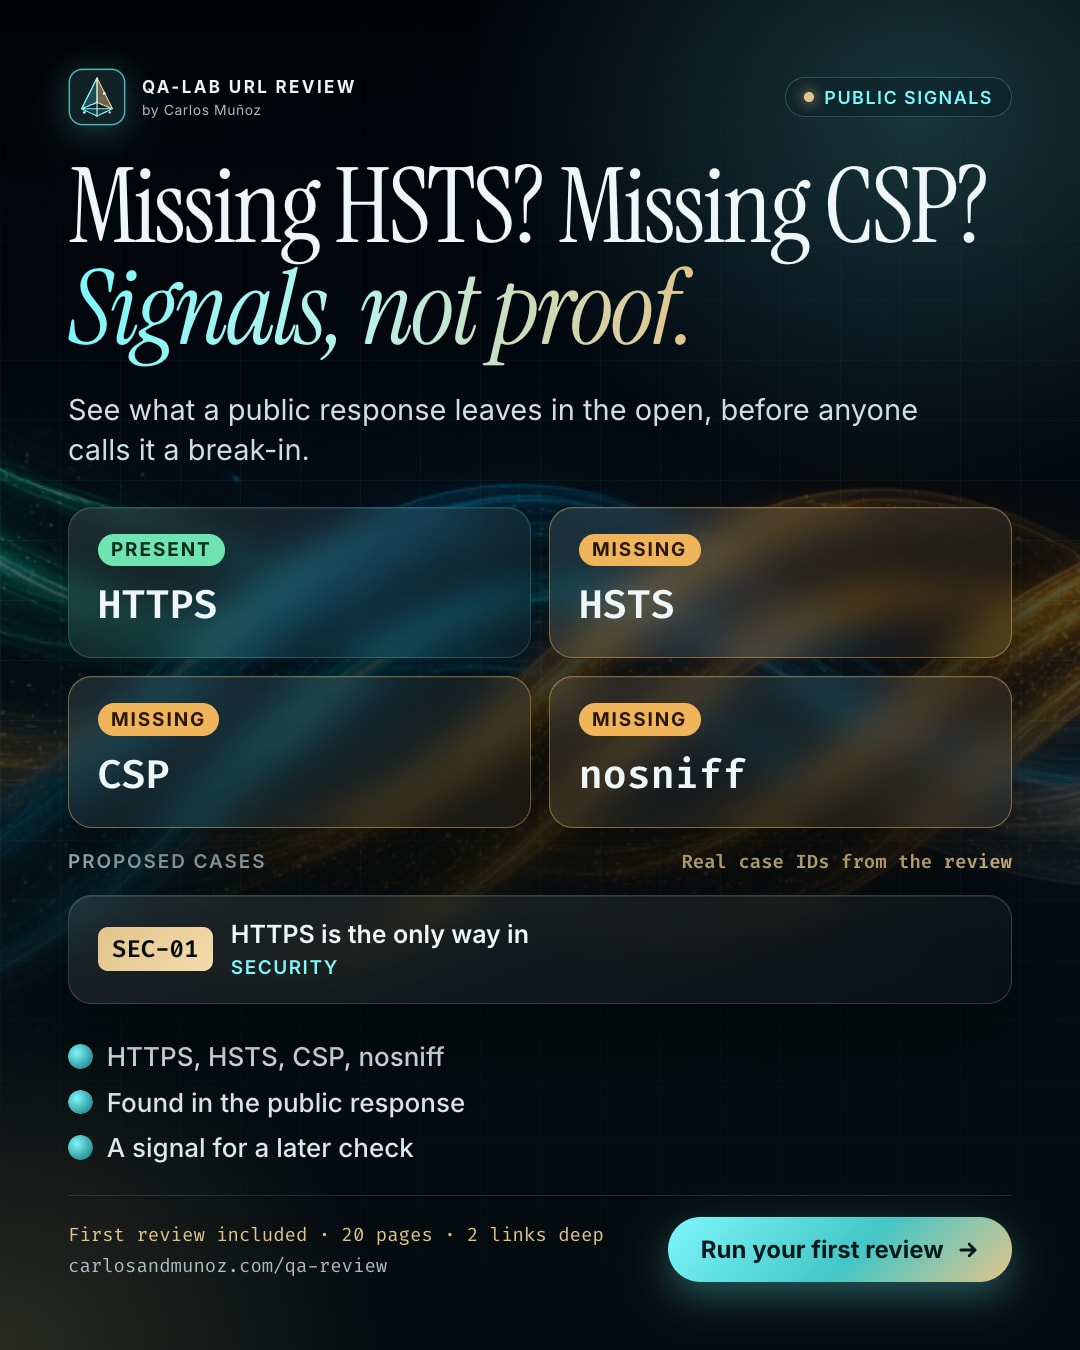
The review lists the security marks a public response shows, like HTTPS, HSTS, CSP, and nosniff, as signals for a later check. It is not a penetration test and not proof of a break-in.→ HTTPS, HSTS, CSP, nosniff → Found in the public response → A signal for a later checkFirst review included · 20 pages · 2 links deep It proposes test cases from a public read. It does not run them, sign in, submit forms, or generate load.Try it on a public URL: carlosandmunoz.com/qa-review.html#SoftwareTesting #QA #TestAutomation #WebSecurity #HTTPHeaders
Your public response headers say more than you think.

The review lists the security marks a public response shows, like HTTPS, HSTS, CSP, and nosniff, as signals for a later check. It is not a penetration test and not proof of a break-in.

→ HTTPS, HSTS, CSP, nosniff
→ Found in the public response
→ A signal for a later check

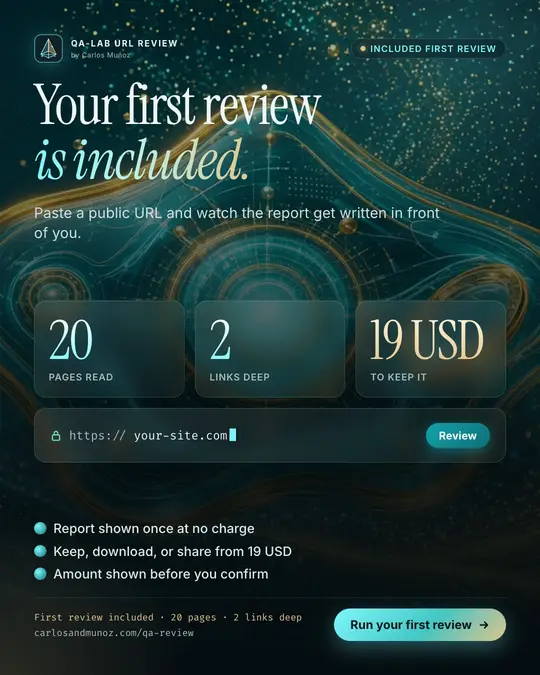
First review included · 20 pages · 2 links deep
It proposes test cases from a public read. It does not run them, sign in, submit forms, or generate load.

Try it on a public URL: https://carlosandmunoz.com/qa-review.html?utm_source=linkedin&utm_medium=social&utm_campaign=url-review-security&utm_content=en

#SoftwareTesting #QA #TestAutomation #WebSecurity #HTTPHeaders
X
Your public response headers say more than you think.

First review included · 20 pages · 2 links deep

https://carlosandmunoz.com/qa-review.html?utm_source=x&utm_medium=social&utm_campaign=url-review-security&utm_content=en
#SoftwareTesting #QA
Instagram
Your public response headers say more than you think.

The review lists the security marks a public response shows, like HTTPS, HSTS, CSP, and nosniff, as signals for a later check. It is not a penetration test and not proof of a break-in.

· HTTPS, HSTS, CSP, nosniff
· Found in the public response
· A signal for a later check

First review included · 20 pages · 2 links deep

Try it on a public URL. Link in bio.

#SoftwareTesting #QA #TestAutomation #WebSecurity #HTTPHeaders
Facebook
Your public response headers say more than you think.

The review lists the security marks a public response shows, like HTTPS, HSTS, CSP, and nosniff, as signals for a later check. It is not a penetration test and not proof of a break-in.

First review included · 20 pages · 2 links deep

Try it on a public URL: https://carlosandmunoz.com/qa-review.html?utm_source=facebook&utm_medium=social&utm_campaign=url-review-security&utm_content=en
TikTok
Your public response headers say more than you think.

First review included · 20 pages · 2 links deep

Try it on a public URL. Link in bio.

#SoftwareTesting #QA #TestAutomation #WebSecurity #HTTPHeaders
YouTube
The review lists the security marks a public response shows, like HTTPS, HSTS, CSP, and nosniff, as signals for a later check. It is not a penetration test and not proof of a break-in.

First review included · 20 pages · 2 links deep

The report shows once at no charge. Keeping, downloading, or sharing it starts at 19 USD, and the amount is shown before you confirm.

Try it on a public URL: https://carlosandmunoz.com/qa-review.html?utm_source=youtube&utm_medium=social&utm_campaign=url-review-security&utm_content=en

Proposes cases · Does not run them · Not a certification

#SoftwareTesting #QA #TestAutomation